Opinion
A Beginner’s Guide to Search Engine Optimization and Improving Page Ranking

Introduction:
In today’s digital era, a strong online presence is paramount for businesses and individuals. Whether you’re a blogger, an entrepreneur, or a small business owner, search engine optimization (SEO) is a fundamental strategy that can help you rank higher in search engine results, drive more organic traffic, and increase your online visibility. In this blog post, we will explore the basics of SEO and provide practical tips to improve your website’s performance in search engines.
Understanding Search Engine Optimization:
Search engine optimization refers to optimizing your website and content to improve its visibility in search engine results pages (SERPs). When you search for a specific query on search engines like Google or Bing, the search algorithms which define the order of displayed results consider various factors. SEO is all about aligning your website and content with these factors to increase your chances of ranking higher in SERPs.
On-Page SEO:
On-page SEO involves optimizing various elements on your website itself to improve its ranking. Here are some important on-page SEO factors and techniques:
Keyword research: Identify relevant keywords and incorporate them appropriately in your website’s content, meta tags, headings, and URLs.
Quality content: Create high-quality, relevant, and engaging content that aims to answer users’ search queries.
Page titles and meta descriptions: Craft enticing and SEO-friendly titles and meta descriptions to increase click-through rates from search results.
URL structure: Use descriptive and concise URLs that include relevant keywords.
Optimized images: Optimize images by compressing their size and using appropriate alt tags.
Off-Page SEO:
Off-page SEO focuses on improving your website’s reputation and authority through external factors. Backlinks from reputable websites, social media signals, and online mentions are crucial for off-page SEO. Here are some effective off-page SEO techniques:
Link building: Create high-quality and relevant backlinks from authoritative websites within your niche.
Social media engagement: Build a strong presence on social media platforms and encourage shares, likes, and comments on your content.
Online directories and listings: Submit your website to relevant online directories and listing platforms to boost your online visibility.
Guest blogging: Contribute guest posts to reputable websites within your industry and include links back to your website.
Technical SEO:
Technical SEO focuses on optimizing the technical aspects of your website to improve its performance and crawlability. Here are some key technical SEO considerations:
Website speed: Ensure your website loads quickly to improve user experience and reduce bounce rates.
Mobile responsiveness: Optimize your website’s design and functionality for mobile devices.
XML sitemaps: Create and submit them to search engines to help them understand and crawl your website more efficiently.
URL canonicalization: Set preferred URLs to avoid duplicate content issues.
SSL security: Install an SSL certificate to make your website secure and improve its search engine rankings.
Conclusion:
Search engine optimization is an ever-evolving practice that can significantly impact your online visibility and success. By implementing the strategies and techniques outlined in this blog post, you can lay a solid foundation for improving your website’s performance in search engine results. Remember that SEO is a long-term process, and staying updated with the latest trends and algorithms is essential. So, invest your time wisely in optimizing your website and enjoy the fruits of increased organic traffic and higher search engine rankings.
- What is search engine optimization (SEO)?
Search engine optimization, or SEO, is the practice of optimizing your website and its content to improve its visibility in search engine results pages (SERPs). It involves various techniques to ensure that search engines understand the relevance and value of your website, ultimately leading to higher rankings and increased organic traffic.
- How does SEO work?
Search engines use algorithms to determine the relevance and quality of websites when a user enters a search query. SEO involves aligning your website and content with these algorithms by optimizing various elements such as keywords, content quality, meta tags, URLs, images, and more. When implemented effectively, SEO improves your website’s chances of ranking higher in search results.
- What is the difference between on-page and off-page SEO?
On-page SEO refers to the optimization techniques applied directly within your website, such as keyword research, content creation, meta tags, and URL structure. Off-page SEO, on the other hand, focuses on external factors that influence your website’s reputation and authority, such as backlink building, social media engagement, and online directory listings.
- How long does it take to see results from SEO efforts?
SEO is a long-term strategy, and results can vary depending on various factors, such as competition, industry, and the extent of optimization efforts. It’s important to be patient and consistent with your SEO efforts as it could take weeks or even months to see noticeable improvements in search rankings and organic traffic.
- Is technical SEO important?
Yes, technical SEO is crucial for optimizing your website’s performance and crawlability by search engines. It focuses on aspects such as website speed, mobile responsiveness, XML sitemaps, URL canonicalization, and SSL security. Proper implementation of technical SEO ensures that search engines can easily access, understand, and rank your website.
- Are backlinks still important for SEO?
Yes, backlinks continue to be an important factor for SEO. Quality backlinks from reputable websites within your industry signal to search engines that your website is trusted and authoritative. Building high-quality backlinks through techniques such as guest blogging and outreach efforts can significantly improve your website’s SEO performance.
- How often should I update my SEO strategy?
SEO is an ever-evolving field, and search engine algorithms continually change. It is recommended to stay up to date with the latest SEO trends and updates, monitor your website’s performance through analytics, and adjust your strategy accordingly. Regularly reviewing and updating your SEO efforts ensures that your website continues to rank well and drive organic traffic.
- Can I do SEO on my own, or do I need to hire an expert?
While basic SEO techniques can be implemented by yourself, hiring an SEO expert or agency can provide you with a deeper understanding and expertise in optimizing your website. They can help analyze your website’s performance, conduct comprehensive keyword research, develop a tailored SEO strategy, and provide ongoing optimization, saving you time and effort in the long run.
- Can SEO guarantee top rankings in search results?
SEO cannot guarantee top rankings in search results as search engines use complex algorithms that consider numerous factors. However, implementing effective SEO practices significantly increases your chances of ranking higher in search results and driving more organic traffic to your website. Regular monitoring, tweaking, and staying abreast of SEO best practices maximize your chances of success.
- Is SEO only for large businesses?
No, SEO is beneficial for businesses of all sizes. Whether you’re a small business owner, a blogger, an entrepreneur, or running an e-commerce store, implementing SEO strategies can help you improve your online visibility, reach your target audience, and compete effectively in the online marketplace. SEO can level the playing field and allow smaller businesses to compete with larger ones in search engine rankings.
Discover more from Remote Work Tips
Subscribe to get the latest posts sent to your email.


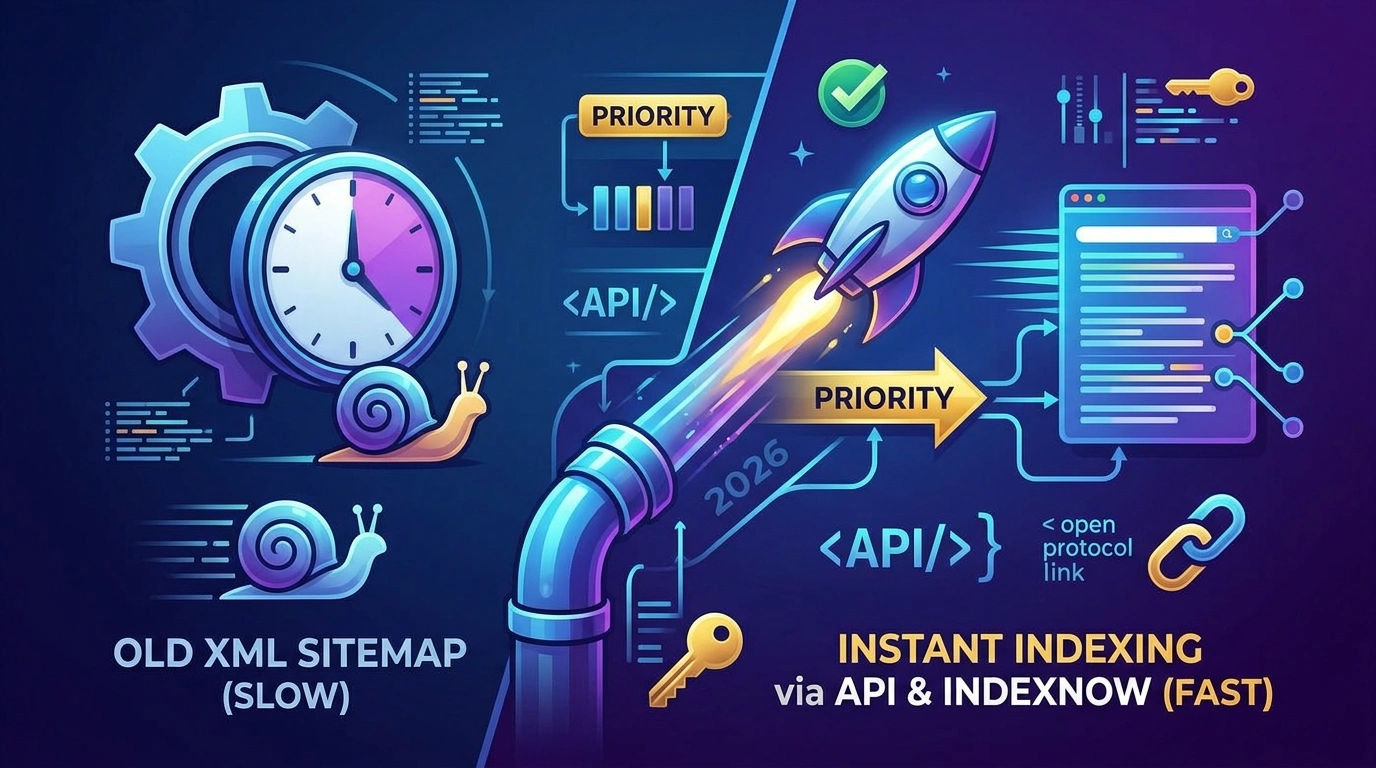
The traditional SEO model of publishing a post and passively waiting weeks for Googlebot to crawl your XML sitemap is dead. In the fast-paced 2026 digital landscape, search engines are allocating their crawl budgets more strictly than ever. For freelance developers and SEO consultants, this shift presents a highly lucrative opportunity: businesses are actively seeking technical specialists who can guarantee their new products, news, and generative AI content are indexed and ranking within hours, not weeks.
By mastering programmatic indexing protocols like the Google Indexing API and IndexNow, you can transition from selling standard “SEO optimization” to offering high-ticket “Instant Indexing Infrastructures.” This guide breaks down exactly how to implement these protocols for your clients, the technical nuances to navigate, and how to monetize this highly demanded skill.
How Do You Achieve Instant SEO Indexing in 2026?
To instantly index website content in 2026, webmasters must bypass passive XML sitemap crawling by programmatically pushing URL updates directly to search engines. For Google, this involves utilizing the Google Cloud Indexing API via a verified Service Account to trigger immediate crawls. For Microsoft Bing, Yahoo, and Yandex, implement the IndexNow protocol by hosting a verification .txt key at the server root and sending HTTP POST requests to automatically notify participating engines of new or updated content.
The Google Indexing API: Pushing Content to the Top
The Google Indexing API allows site owners to directly notify Google’s servers the exact moment a page is added, updated, or removed. Rather than waiting for a scheduled crawl, this API places your URLs in a high-priority queue.
Official vs. Unofficial Capabilities
According to official Google Search Central documentation, the Indexing API is strictly intended for pages containing JobPosting or BroadcastEvent structured data. For sites with highly volatile inventory (like daily job boards or livestream schedules), it keeps search results fresh by pushing updates individually.
However, technical SEO communities have long documented that implementing the API across standard eCommerce products and news articles frequently triggers successful, rapid indexing. While doing this operates in a gray area of Google’s official guidelines, the underlying mechanics remain the same.
Step-by-Step Implementation Framework
- Google Cloud Provisioning: Create a new project within the Google Cloud Console and enable the “Web Search Indexing API.”
- Service Account Creation: Generate a new Service Account and download the JSON key file. This file contains the cryptographic keys your script (or WordPress plugin) needs to authenticate.
- Search Console Authentication: This is the step most beginners miss. You must add the Service Account’s email address as an Owner in the Google Search Console property of the target domain.
- Sending the Payload: Using Node.js, Python, or a CMS plugin, send a POST request to
[https://indexing.googleapis.com/v3/urlNotifications:publish](https://indexing.googleapis.com/v3/urlNotifications:publish)with the target URL and theURL_UPDATEDorURL_DELETEDtype.
Quota Limitations: Google provisions a strict default limit of 200 API calls per day per project. For enterprise clients, you must request quota increases directly through the Cloud Console.
IndexNow: The Open-Source Future of Crawling
While Google maintains its proprietary API, the rest of the search landscape has unified under IndexNow. Supported by Microsoft Bing, Yandex, Seznam.cz, Naver, and Yep, IndexNow is an open-source ping protocol.
The defining advantage of IndexNow is its co-sharing mechanism. Search engines adopting the protocol agree to automatically share submitted URLs with all other participating search engines. You ping one; you update them all.
Implementing the IndexNow Protocol
Setting up IndexNow is significantly lighter than Google’s API, making it an easy “quick win” to offer clients:
- Key Generation: Generate an API key (a minimum of 8 and a maximum of 128 hexadecimal characters).
- Server Root Verification: Host a UTF-8 encoded text file named
{your-key}.txtat the root directory of the client’s website (e.g.,[https://www.example.com/3f2fa233444b4e87a5c40277499c4be4.txt](https://www.example.com/3f2fa233444b4e87a5c40277499c4be4.txt)). The file must contain the exact key string inside. - Triggering the Ping: To submit a single URL, you can fire a simple HTTP GET request.
- Example:
[https://www.bing.com/indexnow?url=https://www.example.com/product-page&key=your-key](https://www.bing.com/indexnow?url=https://www.example.com/product-page&key=your-key)
- Example:
- Batch Submissions: For bulk updates, you can submit up to 10,000 URLs per POST request using a JSON payload containing the
host,key, and anurlListarray.
Actionable Next Steps: Monetizing Your Indexing Skills
Do not sell “Google Indexing API setup” as an hourly task. Package this as a high-value technical infrastructure upgrade.
- The “Instant Index” Audit ($250 – $500): Audit a client’s current indexation ratio (pages published vs. pages indexed in Google Search Console).
- The Technical Implementation ($500 – $1,200): Set up the Google Cloud project, configure the Service Account, generate the IndexNow key, place it on their server, and configure their CMS (via custom PHP or headless architecture) to trigger pings on publish.
- The Retainer ($150/mo): Monitor API error logs, manage the 200-URL daily quota limitations, and maintain the JSON key security.
Frequently Asked Questions (FAQ)
Can I use the Google Indexing API for any type of website?
Officially, Google states the API is only for JobPosting and BroadcastEvent data. Any attempt to abuse the API to spam the index could result in your access being revoked. However, many technical SEOs successfully use it for standard pages, provided the content is high quality and not manipulative.
Do I still need XML sitemaps if I use IndexNow and the Indexing API?
Yes. Both Google and the IndexNow consortium explicitly state that APIs are meant to supplement, not replace, traditional sitemaps. The APIs handle rapid updates for volatile content, while XML sitemaps provide a comprehensive map for the complete structural coverage of your site.
How do I know if my IndexNow ping was successful?
A successful HTTP GET or POST request to the IndexNow endpoint will return an HTTP 200 response code. This confirms the search engine has received the URL, though it does not guarantee immediate inclusion in search engine results pages (SERPs).
Discover more from Remote Work Tips
Subscribe to get the latest posts sent to your email.
careers
The Sovereign Developer: The 5 Most Lucrative Coding Jobs in 2026 (And Why They Pay So Well)
For the past three years, the prevailing tech narrative has been dominated by a singular, slightly hysterical prediction: AI is going to automate software engineering. We were told that generative models would render the human coder obsolete, turning computer science degrees into expensive paperweights.
Welcome to 2026. The reality, as always, is far more nuanced—and significantly more lucrative for those who understood the shift.
It is true that the era of the “syntax translator”—the junior developer who takes highly specified Jira tickets and converts them into standard boilerplate—is fading. In fact, the Bureau of Labor Statistics explicitly projects a 6% decline in traditional “computer programmer” roles by 2034, noting that AI is successfully automating repetitive tasks.
But here is the twist: while programmers are declining, demand for software developers, architects, and quality engineers is surging by 15%, representing roughly 129,200 new openings per year. When AI writes the boilerplate, the human premium shifts away from writing code and toward orchestrating systems, designing architecture, and securing infrastructure.
The highest paying coding jobs in 2026 don’t belong to people who just write code; they belong to the “Sovereign Developers.” These are the engineers who understand how to deploy large language models in production, secure decentralized networks, and build internal platforms that multiply the productivity of entire organizations.
If you want to understand where the real money is in tech today, you have to look at the intersection of capital, complexity, and scale. Let’s dive into the data.
The Methodology: Tracking 2026 Tech Compensation
To identify the most lucrative coding jobs this year, we cannot rely on outdated, pre-AI salary surveys. The market has reorganized itself too quickly.
For this analysis, we synthesized real-time 2026 signed-offer data, crossing quantitative databases with qualitative hiring trends. Our primary sources include:
- Levels.fyi and Glassdoor for self-reported, equity-inclusive total compensation (TC) in Tier 1 and Tier 2 tech hubs.
- KORE1’s 2026 AI Salary Guide for production-grade machine learning compensation.
- Kube Careers Q1 2026 / State of Platform Engineering for the shifting economics of DevOps.
- Robert Half and InterviewPal for baseline corporate architecture ranges.
- BEON.tech’s 2026 Engineering Report for global and nearshore market benchmarking.
A note on compensation: We are focusing on “Total Compensation” (Base Salary + Bonus + Equity/RSUs). While base salaries often hit a ceiling around $250,000, equity is what pushes these roles into the half-million-dollar stratosphere.
Here are the top five most lucrative coding careers in 2026, the economic drivers behind them, and what it takes to break in.
1. AI Infrastructure Engineer (The Model Plumber)
We have officially moved past the “magic trick” phase of Artificial Intelligence. In 2023 and 2024, companies hired researchers to build prototypes. In 2026, companies are hiring AI Infrastructure Engineers to make those prototypes run at scale without bankrupting the company on cloud compute costs.
Why Demand is Exploding
According to Coursera’s 2026 AI Pay Guide, the hype has matured into operational reality. An AI Infrastructure Engineer (or MLOps Engineer) doesn’t necessarily invent new neural network architectures. Instead, they build the pipes. They figure out how to serve a 70-billion parameter open-source model to two million daily active users with sub-100 millisecond latency. They manage GPU clustering, optimize inference engines, and implement RAG (Retrieval-Augmented Generation) pipelines.
Because compute is the most expensive line item on a modern tech company’s P&L, an engineer who can optimize a model’s efficiency by 15% can save a corporation millions of dollars a month. That leverage commands an astronomical premium.
The 2026 Salary Range
- Mid-Level (3-5 years): $170,000 – $260,000 Total Comp
- Senior (6-9 years): $220,000 – $350,000+ Total Comp
- Staff / Principal (10+ years): $350,000 – $600,000+ Total Comp
As KORE1’s recent signed-offer data reveals, inside FAANG (Facebook, Amazon, Apple, Netflix, Google) and premier AI startups like Anthropic and OpenAI, Staff-level AI engineers are routinely seeing total compensation north of $600,000. Even in non-tech hubs like Denver or remote U.S. roles, senior base salaries easily clear $200,000.
The Toolbelt
- Languages: Python, C++, Rust (for performance-critical bottlenecks).
- Frameworks/Tools: PyTorch, vLLM, TensorRT, Triton, LangChain.
- Infrastructure: Kubernetes, CUDA programming, Vector Databases (Pinecone, Weaviate).
2. Platform Engineer (The Evolution of DevOps)
If you are still calling yourself a DevOps Engineer, you might be leaving 20% of your potential salary on the table. The breakout role of the last two years has undeniably been the Platform Engineer.
Why Demand is Exploding
For years, “DevOps” was less of a role and more of a chaotic culture where software engineers were suddenly forced to manage their own cloud infrastructure, leading to massive burnout. Enter Platform Engineering.
Instead of fixing individual deployment pipelines, Platform Engineers build an “Internal Developer Platform” (IDP). They treat their fellow developers as their customers, building self-service portals where a software engineer can spin up a secure, compliant cloud environment with a single click.
Gartner accurately predicted that by 2026, 80% of large engineering organizations would have dedicated platform teams. Because a great platform engineer accelerates the output of every other developer in the company, their multiplier effect is massive.
The 2026 Salary Range
- Average Base Salary: $172,038
- Senior Total Comp: $220,000 – $290,000
- The “Platform Premium”: According to Q1 2026 data from Kube Careers, Platform Engineers earn an average of 20% to 27% more than traditional DevOps engineers ($172K vs. $143K), simply because the role requires a broader, product-oriented mindset.
The Toolbelt
- Languages: Go, Python, TypeScript.
- Frameworks/Tools: Backstage (Spotify’s IDP framework), Crossplane, ArgoCD.
- Infrastructure: Kubernetes (absolute mastery required), Terraform, advanced CI/CD.
3. Data Architect (The Moat Builder)
In the age of ubiquitous AI, the algorithms are largely commoditized. Everyone has access to the same foundational models from OpenAI, Google, or Meta. Therefore, a company’s only remaining competitive moat is its proprietary, internal data. If your data is messy, your AI is useless.
Why Demand is Exploding
The Data Architect is the visionary who structures how an organization collects, governs, and utilizes petabytes of information. They are moving away from clunky, centralized data warehouses and toward modern “Data Mesh” architectures—treating data as a decentralized product.
As noted by InterviewPal’s 2026 Benchmarks, competencies in real-time data streaming and multi-cloud architectures add 15% to 25% salary premiums to an offer. You aren’t just writing SQL; you are designing the nervous system of the enterprise.
The 2026 Salary Range
- Median Total Comp: $203,250
- Top 10% (Senior/Enterprise): $400,000+ Total Comp
- Geographic Arbitrage: Remote Data Architects living in tier-2 cities are frequently securing San Francisco-level base salaries ($180,000 – $280,000) because the talent pool capable of bridging data engineering and machine learning workflows is incredibly shallow.
The Toolbelt
- Languages: SQL (advanced), Python, Scala.
- Frameworks/Tools: Apache Kafka, Flink, Spark, dbt (Data Build Tool).
- Infrastructure: Snowflake, Databricks, AWS Redshift/GCP BigQuery.
4. Cybersecurity Architect / Security Engineer (The Shield)
As code generation tools allow developers to ship software faster than ever, the surface area for cyber attacks has expanded exponentially. Furthermore, AI agents are now being weaponized by threat actors to find zero-day vulnerabilities at machine speed.
Why Demand is Exploding
The Cybersecurity Architect is no longer just the “department of no.” They are fundamental to business continuity. These professionals design “Zero Trust” networks and secure the sprawling, complex cloud environments deployed by the engineers mentioned above.
A 2026 Unihackers Salary Guide highlights that there are still millions of unfilled cybersecurity positions globally. The shift toward securing LLM supply chains (ensuring AI models aren’t poisoned with malicious training data) has created a hyper-niche, hyper-lucrative subfield. When the alternative is a $50 million ransomware payout and a destroyed reputation, companies do not bargain hunt for security architects.
The 2026 Salary Range
- Security Engineer (Mid): $150,000 – $247,000 Base
- Cloud Security Architect: $170,000 – $220,000 Base
- CISO (Chief Information Security Officer): $220,000 – $420,000+ Base (Total comp routinely exceeds $500K in enterprise).
The Toolbelt
- Languages: Python, Go, C (for reverse engineering).
- Frameworks/Tools: Cloud Security Posture Management (CSPM), SIEM tools, Identity and Access Management (IAM).
- Methodologies: Zero Trust Architecture, DevSecOps, Penetration Testing, AI Threat Modeling.
5. Cloud/Distributed Systems Architect (The Orchestrator)
While “Cloud Architect” might sound like a legacy title from 2018, the 2026 version of this role is practically unrecognizable. It is no longer about migrating on-premise servers to AWS. It is about managing terrifying levels of distributed complexity.
Why Demand is Exploding
Companies are now running “multi-cloud” strategies to avoid vendor lock-in, while simultaneously pushing compute to the “edge” (closer to the user) to support real-time AI features. The Cloud Architect designs systems that can survive entire regional data center outages without the user ever noticing.
According to Robert Half’s 2026 Tech Salary Data, cloud architecture remains foundational. They must balance high availability with ruthless cost optimization. A great Distributed Systems Architect pays for their own salary in their first month just by optimizing cloud egress fees and compute instances.
The 2026 Salary Range
- Mid-Level Base: $135,000 – $170,000
- High/Senior Base: $162,750 – $200,000+
- Total Comp: Frequently crosses $250,000 to $300,000 when factoring in equity at major tech firms and tier-1 consultancies.
The Toolbelt
- Languages: Java, Go, Rust.
- Frameworks/Tools: HashiCorp Stack (Terraform, Consul, Vault), gRPC.
- Infrastructure: Deep, native expertise in AWS, GCP, or Azure; Distributed consensus algorithms (Raft/Paxos).
2026 Coding Jobs Landscape: A Comparative View
| Role | Median Total Comp (US) | Primary Economic Driver | Barrier to Entry | Career Velocity |
| AI Infrastructure | $250,000+ | AI scale & compute optimization | Very High | Explosive |
| Platform Engineer | $210,000+ | Org-wide developer productivity | High | High |
| Data Architect | $203,000+ | Proprietary data as a business moat | High | Steady / High |
| Cybersecurity Arch. | $210,000+ | Cloud expansion & AI threat vectors | High (Requires high trust) | High |
| Cloud Architect | $190,000+ | Multi-cloud complexity & cost control | Medium / High | Steady |
(Note: Data aggregated from Levels.fyi, Kube Careers, and KORE1 Q1 2026 reports. Figures represent estimated medians for senior-level talent including equity).
How to Break In: Advice for Ambitious Tech Professionals
If you are looking at these numbers and wondering how to pivot your career, the advice for 2026 is fundamentally different than it was a decade ago. You cannot just “learn to code” in a vacuum anymore. You must learn to architect.
Here is how you upskill into these premium tiers:
1. Shift from “Syntax” to “Systems Thinking”
Stop defining yourself by the programming language you use. Being a “React Developer” or a “Java Developer” is a vulnerable position in an era of AI code generation. Instead, become an expert in the systems those languages run on. Understand networking, memory management, distributed databases, and cloud economics. AI is great at writing a discrete function; it is currently terrible at designing a resilient, SOC2-compliant microservices architecture.
2. Learn the Language of the Business
The highest-paid engineers don’t talk about code; they talk about leverage. A Platform Engineer commands $200,000 because they can say: “My internal portal reduced developer onboarding time from 3 weeks to 3 hours, saving the company $1.2M annually.” Learn to translate your technical implementations into P&L (Profit & Loss) impact.
3. Embrace the Open Source AI Ecosystem
You do not need a Ph.D. in mathematics to work in AI today. You need to understand implementation. Spend your weekends fine-tuning open-source models (like LLaMA 3 or Mistral) on your own data. Learn how to use vector databases. The gap between “traditional software engineer” and “AI engineer” is bridged by understanding the modern MLOps stack.
4. Master Cloud Economics (FinOps)
In the era of zero-interest rate phenomena (ZIRP), companies didn’t care about cloud bills. In 2026, efficiency is everything. If you can walk into an interview and demonstrate how your architectural decisions reduced AWS spend by 30% while improving performance, you write your own ticket.
The Broad View: Code as Capital
The panic surrounding the death of the software engineer was misplaced. What died was the commoditized coder.
As we look at the landscape of 2026, it is clear that programming is no longer viewed as a blue-collar digital trade. It has evolved into high-stakes capital allocation. When you deploy code today, you are deploying the autonomous agents, data pipelines, and security protocols that constitute the actual metabolic system of the modern corporation.
The roles that command a quarter-million dollars or more are those that require intense human judgment, strategic foresight, and an understanding of complex, interlocking systems. The AI will write the lines. But it is the Sovereign Developer who will build the world.
Frequently Asked Questions (FAQ)
Q: Will AI eventually automate these high-paying architecture jobs too?
A: Eventually is a long time, but architecture requires understanding ambiguous business requirements, navigating corporate politics, and balancing competing trade-offs (e.g., cost vs. latency vs. security). Current AI excels at deterministic tasks with clear boundaries, not ambiguous, high-stakes system design.
Q: Do I need a degree to get these jobs in 2026?
A: According to the BLS, a bachelor’s degree remains the standard entry point. However, in disciplines like Platform Engineering and Cloud Architecture, undeniable proof of work (open-source contributions, massive system design experience, top-tier certifications like AWS Solutions Architect Professional or Kubernetes CKA) routinely supersedes formal education requirements.
Q: What is the highest paying coding job without a management title?
A: Staff and Principal AI/ML Infrastructure Engineers. These are “Individual Contributor” (IC) roles that do not manage people, yet they frequently out-earn mid-level engineering managers and directors, easily pulling $400K+ in total compensation at top-tier tech firms.
Q: I’m a mid-level Full-Stack Developer. What is my fastest path to a $200K+ role?
A: The most logical lateral move is into Platform Engineering or Cloud Architecture. Your frontend/backend experience gives you empathy for the developers you will be building tools for. Upskill heavily in Kubernetes, Go, and Infrastructure as Code (Terraform), and reposition your resume around “developer experience” and “system reliability.”
Discover more from Remote Work Tips
Subscribe to get the latest posts sent to your email.
Imagine logging into Google on a Tuesday morning to check your own name — a routine vanity search, the kind every self-employed professional quietly performs — and finding, nested inside the results, a PDF you recognise instantly. It is your Form 1040. Your Social Security number. Your adjusted gross income. Your spouse’s name. Uploaded to Fiverr last autumn when you hired a bookkeeper. Indexed. Publicly accessible. Sitting there, open to anyone with a browser and a moderately curious mind. You didn’t consent to a Google listing. You consented to a private transaction on a trusted marketplace. The distinction, as Fiverr is now discovering to its considerable cost, matters enormously.
This is not a hypothetical scenario. For hundreds — possibly thousands — of freelancers and their clients, it is an unfolding reality. On April 14, 2026, a security researcher operating under the pseudonym @morpheuskafka published findings on Hacker News that detonated inside the cybersecurity community like a slow-burning grenade finally going off. Fiverr, the Tel Aviv–headquartered gig-economy giant worth roughly $1 billion in market capitalisation, had left an extraordinary volume of private user documents — tax returns, driver’s licenses, server credentials, VPN passwords, API keys, client contracts — publicly accessible and fully indexed by Google.
Fiverr’s response was swift, corporate, and, to many observers, deeply inadequate. “This is not a cyber incident,” the company announced on X. The platform did not explain why a completed tax return was searchable on the world’s most powerful search engine. It did not apologise. It did not commit to a timeline for remediation. It invoked user consent.
That invocation deserves far more scrutiny than it has so far received.
The Incident: A Timeline of Exposure and Silence
The architecture of this failure is, technically speaking, straightforward — which is precisely what makes it so damning.
Fiverr uses Cloudinary, a widely adopted cloud-based media management platform, to process, store, and deliver files exchanged between freelancers and clients during project workflows. When a business owner hires a developer on Fiverr and sends a PDF through the platform’s messaging system — containing, say, database credentials or server login details — that file is uploaded to Cloudinary and assigned a URL for delivery.
Cloudinary effectively acts like Amazon S3 in this configuration, serving assets directly to the web client. And like S3, it has built-in support for signed, expiring URLs — time-limited links that require cryptographic authentication to access. This is not exotic engineering. It is a standard, documented feature that Cloudinary has offered for years, analogous to AWS S3 presigned URLs that any competent cloud architect would reach for when handling sensitive content.
Fiverr opted to use public URLs instead of signed ones for sensitive client-worker communication. Moreover, the platform appears to have been serving public HTML somewhere that links to these files, meaning Google’s crawler could follow those links, fetch the PDFs, and index their full contents.
The researcher reported this to Fiverr’s security team 40 days before going public. No response came. Hours after the Hacker News post hit 600+ points, the files were still live.
The documents exposed were not theoretical. The Cybernews research team analysed the leak and confirmed the claims appear valid, noting that essentially all files shared between service buyers and sellers — including personal identity documents, sensitive contracts, passwords, and API keys shared with contractors — were affected.
Among the documents discoverable through the exposed storage was, in a moment of spectacular irony, Fiverr’s own ISO 27001 certification for information security excellence — which had expired four months prior.
The reaction on Hacker News was not the usual technical one-upmanship. “Extremely bad stuff here. Can’t believe it’s been 7 hours now and you can still pull up people’s complete prepared tax returns right from a Google search. This should be a business-ending breach of trust and good practices, but I worry there’s probably a lack of regulatory might or will to make anything happen,” one user wrote. The sentiment was widely shared. The post climbed to the forum’s front page. The credentials remained searchable.
The Technical Deep Dive: Why This Is Not “Just User Error”
Fiverr’s statement pivots on the concept of consent. Users, the company argues, shared these documents voluntarily during transactions. This framing conflates two categorically different acts: the act of sharing a file with a counterparty inside a private platform, and the act of publishing that file to the open internet.
When you hand your passport to an airline check-in agent, you consent to identity verification. You do not consent to having your passport photocopied and posted on a public noticeboard. The distinction is not semantic. It is the entire premise of modern data protection law.
Fiverr’s entire file delivery system uses public, unsigned Cloudinary URLs. Every PDF and image exchanged between freelancers and clients through Fiverr’s messaging was assigned a permanent public link. Google crawled those links and indexed their contents. The workflow requires no hacking, no credential theft, no sophisticated exploit. It requires a Google search.
Consider a common transaction: a business owner hires a freelancer on Fiverr to configure their VPN or manage their AWS infrastructure. To give the freelancer access, they send a PDF through Fiverr’s messaging with the credentials — server IP, username, password, SSH key, or VPN configuration file. Fiverr routes that file through Cloudinary. The file gets a permanent public URL. That URL ends up on a publicly indexed HTML page. Google finds it. The credentials are now in search results.
A leaked password in a PDF is worse than a leaked password in a database breach. Database breaches typically expose hashed passwords — an attacker must still crack them, and modern bcrypt or argon2 hashes require serious computational effort. Most of these credentials are never rotated. The freelancer finishes the job. The business owner moves on. The password stays the same for months or years. The Fiverr message thread sits in their account history, and the PDF sits on Cloudinary’s CDN, indexed and waiting.
This is not a user error. This is a deliberate engineering decision — the choice to use permanent public URLs instead of authenticated, expiring ones — that had predictable, foreseeable, and catastrophic consequences for the people who trusted the platform with their most sensitive professional and personal documents.
The signed-URL solution is not aspirational. It is Table-Stakes Infrastructure. Cloudinary’s own documentation describes the feature in straightforward terms, noting it supports access-controlled delivery with configurable expiration. AWS has offered the equivalent for over a decade. The cost of implementation is negligible. The cost of omission, as we are now discovering, is incalculable.
Fiverr’s Response — And Why It Falls Catastrophically Short
Fiverr’s official statement, issued in reply to Cybernews’ post on X, read: “To be clear, this is not a cyber incident. Fiverr does not proactively expose users’ private information. The content in question was shared by users in the normal course of marketplace activity to showcase work samples, under agreements and approvals between buyers and sellers. This type of content requires the buyer’s consent before it can be uploaded. As always, any request to remove content is handled promptly by our team.”
Let us examine each clause.
“This is not a cyber incident.” The phrase “cyber incident” has no universally agreed legal definition. What is unambiguous, however, is that the FTC Safeguards Rule — which covers “financial institutions,” including tax preparers — requires covered entities to implement and maintain a comprehensive security program to protect customer financial information. A tax return appearing in Google search results is not a “work sample.” It is a compliance catastrophe.
“Content was shared by users…under agreements and approvals between buyers and sellers.” This is technically accurate and entirely beside the point. User consent to share a file with a counterpart within a private transaction is not consent to expose that file to the global internet. GDPR’s Article 5 principle of purpose limitation explicitly prohibits processing data “in a manner that is incompatible with those purposes.” A tax preparer’s client who shares a Form 1040 to facilitate a service consents to exactly that purpose — not to publication on Google.
“Any request to remove content is handled promptly by our team.” This is the most troubling assertion of all. It implies that the remediation framework for a systematic infrastructure misconfiguration is reactive, individual, request-by-request removal. The responsible answer to this kind of exposure is immediate, platform-wide remediation: converting all existing public URLs to signed ones, crawling for Google-indexed documents, and filing mandatory breach notifications where required. Waiting for individual users to discover their data is in Google and file removal requests is not a security posture. It is an abdication of one.
Aras Nazarovas, an information security researcher at Cybernews, was unequivocal: “This is a major security lapse by Fiverr, due to the links being publicly accessible and indexable. A lot of resources are already being indexed by Google.”
The company’s silence during the 40-day responsible disclosure window compounds the failure. Responsible disclosure — the practice of privately notifying an organisation of a vulnerability before going public — is a cornerstone of ethical security research. The researcher stated that Fiverr was notified of the issue via its designated security contact approximately 40 days prior to public disclosure, but received no response. In that window, thousands of documents remained indexed and accessible.
The Broader Stakes: A $1.5 Trillion Gig Economy’s Trust Problem
Fiverr is not a niche operator. It is among the largest platforms in a global gig economy that Goldman Sachs and other analysts estimate could surpass $1.5 trillion in total value by the end of the decade. Its user base includes freelancers and clients in over 160 countries. Many of those users — tax preparers, accountants, legal document preparers, healthcare administrators — operate in heavily regulated industries where the secure handling of client data is not merely good practice but a legal obligation.
The researcher behind the original disclosure noted that Fiverr itself actively buys Google Ads for tax-filing keywords like “form 1234 filing,” directing clients to its platform — meaning the company is actively recruiting users to conduct precisely the kind of work that generates the sensitive documents now appearing in search results. Without adequate security, the company might be violating the GLBA (Gramm-Leach-Bliley Act) and the FTC Safeguards Rule, which require tax preparers to protect client financial data.
The GLBA exposure alone is significant. Under the FTC’s updated Safeguards Rule, financial institutions — a category that expressly includes tax preparers — are required to implement technical safeguards appropriate to the sensitivity of the data they handle. “Appropriate safeguards” for tax returns does not include permanent public CDN URLs.
The regulatory exposure extends beyond the United States. Under GDPR, data processors are required to implement “appropriate technical and organisational measures” to ensure security appropriate to the risk. The supervisory authorities in EU member states — the Irish Data Protection Commission and Germany’s BfDI among them — have demonstrated increasing willingness to pursue maximum fines. The UK’s ICO has similarly grown more aggressive since GDPR’s 2018 enactment. Fiverr’s European user base is substantial.
For the gig economy writ large, the implications are harder to quantify but potentially more consequential. Platforms like Upwork, Freelancer.com, and Toptal rely on the same basic architecture: cloud-based file exchange between clients and contractors, mediated by a trusted platform. Every one of them should be auditing their CDN configurations this week. Not because they necessarily have the same vulnerability — but because the research community has now demonstrated that this attack surface is real, exploitable, and far more visible than anyone imagined.
The trust economics of platform marketplaces are fragile. An Upwork user does not merely trust Upwork with their credit card details. They trust the platform with their intellectual property, their financial documents, their business credentials, their identity verification documents. That trust is not a commodity. It is the entire product. When it fractures, the fracture is rarely recovered cheaply or quickly.
What Needs to Change — And Why Voluntary Compliance Is No Longer Sufficient
The Fiverr incident is a case study in what happens when data security is treated as a compliance checkbox rather than an engineering imperative. It demands structural responses at three levels.
At the Platform Level: Mandatory implementation of signed, expiring URLs for all user-generated content involving PII should be a baseline requirement — not a best-practice recommendation. The technology exists. The cost is marginal. The decision to use permanent public URLs for sensitive documents is, in this environment, indefensible. Platforms should also conduct automated content classification at upload, flagging documents that contain Social Security numbers, passport data, or financial account information for enhanced access control. The EU’s AI Act creates a framework for exactly this kind of automated high-risk processing — legislatures could extend similar logic to cloud storage configurations.
At the Regulatory Level: The FTC’s Safeguards Rule should be amended to include explicit requirements for cloud storage configuration standards for covered financial institutions using third-party CDN or media management services. The current rule’s technology-neutral language — while appropriate for most purposes — creates ambiguity that platforms exploit. GDPR’s supervisory authorities should, and almost certainly will, initiate investigations. Data protection authorities in the UK, Ireland, and Germany have all demonstrated their willingness to act in cross-border cases. Fiverr’s dual exposure to US and EU regulatory frameworks means the liability calculus is substantially more complex than its current public statement acknowledges.
At the Industry Level: Independent security audits for any platform handling sensitive professional documents should become a condition of operating in the jurisdictions with the strongest data protection regimes. The irony of Fiverr’s expired ISO 27001 certification appearing among its publicly indexed documents is not merely symbolic — it is a reminder that certification bodies and regulatory frameworks need robust re-certification requirements with real teeth. An expired security certification is not a certification. It is a liability.
The Hacker News community — which functions, imperfectly but meaningfully, as a real-time security audit of the commercial internet — surfaced this vulnerability within hours of disclosure. The researcher who found it waited forty days for a corporate response and received none. The formal regulatory architecture that should catch these failures before they become public disasters manifestly did not. Something is broken in the system. And it is not only Fiverr’s CDN configuration.
Conclusion: The Gig Economy Cannot Afford to Be Cavalier with Trust
There is a particular cruelty to data exposure incidents on labour platforms. The people most affected are frequently the most economically vulnerable — freelancers building client books, small business owners outsourcing tasks they cannot afford to handle in-house, tax preparers in low-margin practices who took to Fiverr because the economics made sense. They are not sophisticated enterprise clients with dedicated legal and compliance teams. They trusted a billion-dollar platform to protect them. The platform did not.
Fiverr’s statement that “this is not a cyber incident” may survive a narrow legal review. It will not survive the reputational one. When a user’s Form 1040 appears in Google search results — when their driver’s license, their client contracts, their server passwords are accessible to anyone curious enough to type a moderately precise query — the semantic argument about whether this constitutes a “cyber incident” rings hollow to the people whose lives are on the page.
The gig economy is, at its best, a mechanism for democratising access to professional opportunity. It functions on the premise that digital platforms can be trusted intermediaries — more reliable, more transparent, more accountable than informal labour markets. That premise is contingent on security. When it fails, what fails with it is not just one company’s reputation, but the broader architecture of trust on which an entire economic model depends.
Fiverr has an opportunity to do more than deny. It can remediate transparently, notify affected users, engage regulators proactively, and commit — in writing, with timelines — to a signed-URL architecture for all future user content. That would be leadership. The alternative — defensive statements, reactive removals, regulatory investigation, and the slow erosion of user confidence — is considerably more expensive.
The files may eventually disappear from Google’s index. The lesson, if Fiverr and its peers have the wisdom to absorb it, should not.
Discover more from Remote Work Tips
Subscribe to get the latest posts sent to your email.


Top 6 Payment Solutions for Freelancers Faster Than Banks
Midway through a project in Milan, a freelance UX designer named Elena watched her rent payment bounce. The client’s bank...


10 Freelancing Tips for Landing Projects in the AI Era
The Market Split No One Warned You About In February 2026, a mid-career graphic designer in Austin posted to a...


The Sovereign Developer: The 5 Most Lucrative Coding Jobs in 2026 (And Why They Pay So Well)
For the past three years, the prevailing tech narrative has been dominated by a singular, slightly hysterical prediction: AI is...


Top 10 Most Demanded Freelance Skills in 2026
The Trillion-Dollar Talent Shift Nobody Is Talking About Honestly There is a number that should stop every career-minded professional in...


Fiverr Denies ‘Major Security Lapse’ Despite Private User Data Appearing in Google Search
Imagine logging into Google on a Tuesday morning to check your own name — a routine vanity search, the kind...


4 Must-Have Skills Every Nomadic Founder Needs to Build a Successful Online Business
Want to work from anywhere? I know this because I’ve been on both sides of that line. From Trucking Routes...


Unlock 50% More Billable Hours: Top 5 AI Tools Every Freelancer Needs in 2026
Here is a number worth sitting with: AI-enabled freelancers now save an average of eight hours per week and earn...


Challenges to Freelancers in the Age of 5G and AI in 2026
The Morning the Rates Dropped At 6:47 on a Tuesday morning in Bengaluru, Arjun Mehta refreshed his Upwork dashboard and...
-

 blogging5 years ago
How to Use Social Media to Promote Your Blog
-

 freelance5 years ago
6 Future-Focused Skills Freelance Creatives Can’t Afford to Ignore
-

 social media5 years ago
How to Learn Social Media Without Getting Scammed
-

 freelance9 months ago
The Economics of Remote Work: How Hybrid Models Are Reshaping Global Productivity
-

 blogging5 years ago
20 Best Freelance Marketplaces for Freelancers in 2022 to Make Money
-

 freelance5 years ago
7 Highest Paying Freelance Jobs For Earning A Steady Income
-

 Digital Banking5 years ago
Pakistan Consumer Confidence Index increased by 8.8% in Q4 2021
-

 blogging5 years ago
30 “Proven” Ways to Make Money Online Blogging with WordPress